
How many types of ad fraud techniques are you aware of? Of those that you know of, can you explain how each works, and how they threaten your organization?
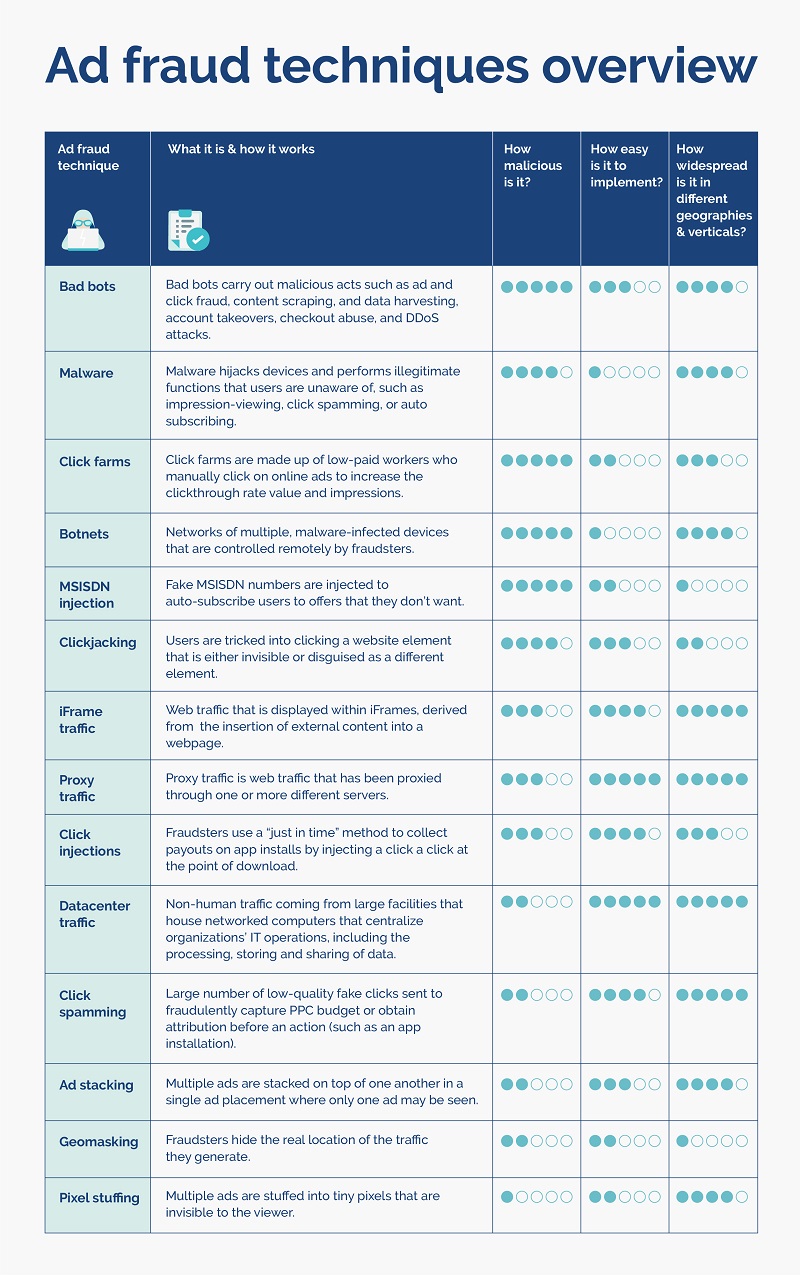
Being able to fight ad fraud demands an understanding of the types of techniques fraudsters use day in, day out. In this article, we go through fourteen of the most common types of ad fraud techniques, how they work, what threats they pose, and tips for preventing them from becoming a threat to your organization.
14 Ad fraud techniques and how to prevent them
Not only is the occurrence of ad fraud on the rise, but so too are the ways it’s carried out. Below, we go through how each ad fraud technique works, the risks they pose to your organization, and how to prevent them from damaging your ad campaigns.
Index
- Ad stacking
- Bad bots
- Botnets
- Click farms
- Click injections
- Clickjacking
- Click spamming
- Datacenter traffic
- Geomasking
- iFrame traffic
- Malware
- MSISDN injection
- Pixel stuffing
- Proxy traffic
Bad bots
What are bad bots?
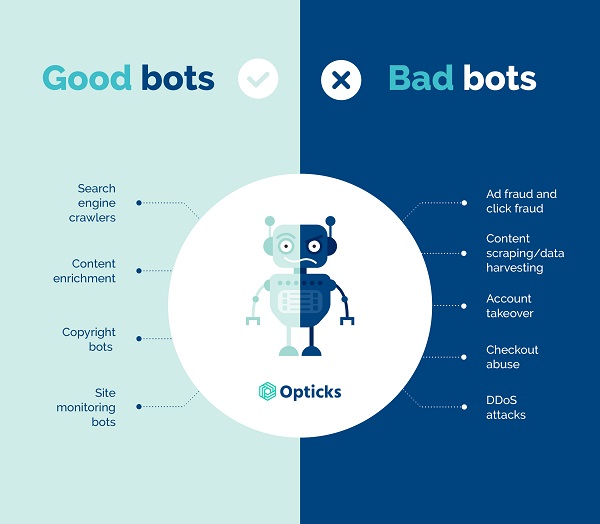
Bad bots are bots that carry out malicious acts such as ad and click fraud, fake clicks, fake impressions. Other actions include content scraping, data harvesting, account takeovers, checkout abuse, and DDoS attacks.
How do bad bots work?
Bad bots are constantly maturing and evolving into more sophisticated threats. They’re progressively able to emulate real human workflows across web applications to appear as real users. Bots make it look like an ad is receiving a ton of impressions, when in fact a bot is simply scanning it.
What are the threats posed by bad bots?
Bad bots are extremely malicious. They can generate a huge number of fake clicks to completely drain ad budgets quickly and from afar. Beyond that, bad bots contribute to impression fraud, click fraud, lead fraud, subscription fraud, attribution fraud, and skewed analytics
They can also swiftly serve malware to users, steal data and credentials, plagiarize content, and siphon thousands of dollars from your budget. Learn how to detect a bot before it drains your campaigns.
Related techniques: Datacenter traffic and proxy traffic.
Malware
What is malware?
Malware hijacks devices to perform illegitimate functions that users are unaware of. Specifically, this occurs when fraudsters sneak malicious code into installations.
How does malware work?
For example, unaware users install fraudulent apps/software development kits (SDKs), which load ad impressions outside of the user’s visible area of a webpage. The app or SDK will then fraudulently trigger clicks or perform lead generation activities. Apps outside of the Google Playstore are an important vehicle of this ad fraud technique, often distributed by fraudulent app publishers.
Users may realize that their devices have become hijacked by malware when they notice an increase in data usage, battery drainage, and unwanted subscriptions through their carrier billing.
What are the threats posed by malware?
Malware hijacks devices to perform impression fraud, click fraud, lead fraud, subscription fraud, attribution fraud, and can also skew data and analytics.
Malware can also waste media budgets by creating fake clicks and impressions. It can also skew engagement metrics and incorrectly influence future ad spending decisions.
Related techniques: Bad bots, click spamming, pixel stuffing, ad stacking, click injection, MSISDN injection, and geomasking.
Click farms
What are click farms?
Click farms (and lead farms) consist of low-paid workers who manually click on online ads to increase clickthrough rate value and impressions.
Farms can also become lead farms when fraudsters use them to carry out lead generation fraud. See our dedicated guide to click farms for a deeper breakdown. Humans fill out forms with randomized information (or belonging to real people, without their knowledge or consent).
How do click farms work?
Click farms vary in sophistication, but the concept is simple. Imagine a large room filled with people sitting in front of computers and/or phones. In other words, they sit there manually clicking on ads to drain ad budgets.
What are the threats posed by click farms?
A click farm’s main aim is to drain ad budgets, and it’s done in a relatively easy way. Click farms cause impression fraud, click fraud, lead fraud, subscription fraud, and attribution fraud, and they skew your data and analytics.
Plus, click farm operations are usually based in countries specifically where there is little regulation against this type of fraudulent activity, such as China, India, and the Philippines, making it even more difficult to hold them to account.
Related techniques: Geomasking and click spamming,
Botnets
What are botnets?
Botnets are a network of multiple malware-infected devices, and fraudsters control them remotely to carry out malicious activities such as marketing fraud, credential leaks, DDoS attacks, and data theft.
In short, a botnet’s objective is to infect as many connected devices as possible and use them for automated, repetitive tasks that users cannot detect.
How do botnets work?
Specifically, botnets use infected devices to partially override web browsers to divert fraudulent traffic to click on online ads. By using only a small fraction of web browsers, they’re able to remain invisible to the user.
What are the threats posed by botnets?
Botnets are highly malicious. The number of fake clicks they can generate can completely drain ad budgets in a very short amount of time and can do so from afar. In totality, they can drive impression fraud, click fraud, subscription fraud, and attribution fraud. Botnets also lead to skewed analytics, and can also break through passwords and security questions with very little effort.
Related techniques: Hijacked devices, clicks pamming, pixel stuffing, ad stacking, geomasking, and bad bots.
MSISDN injection

Example of MSISDN injection
What are MSISDN injections?
MSISDN injections aren’t always malicious — in fact, some operators use them to enrich transactions in direct carrier billing. However, however, fraudsters inject fake MSISDN numbers to auto-subscribe unaware users to offers that they might not necessarily want.
How do MSISDN injections work?
MSISDN injections use sophisticated pieces of automated software that emulate the journey of the user. In particular, infected devices declare a user-agent header not normally associated with human activity. Headers containing MSISDN information are a clear indication of fraud.
What are the threats posed by MSISDN injections?
MSISDN injections lead to subscription fraud. Experts consider them very malicious, and they’re technologically difficult for fraudsters to enact. They are also associated with very localized attacks.
Related techniques: Bad bots, botnets, malware, geomasking, proxy traffic, and datacenter traffic.
Clickjacking

What is clickjacking?
Clickjacking occurs when fraudsters fool users into clicking a website element that’s either invisible or disguised as something else. This ad fraud technique tricks users into downloading malware, visiting unsafe websites, giving away personal credentials, authorizing transfers of money, and activating cameras and microphones.
How does clickjacking work?
Fraudsters place invisible or disguised malicious links or HTML elements over a website’s user interface inside an iFrame. The user believes they’re clicking the visible page, but they’re actually clicking the invisible or disguised element that fraudsters placed on top of it.
What are the threats posed by clickjacking?
Clickjacking is a malicious ad fraud technique since it is a form of attribution fraud. It can also steal people’s personal information, withdraw money, and lead users to insecure web pages. It’s also a relatively easy method of ad fraud for fraudsters to deploy and is usually quite localized.
Related techniques: N/A.
iFrame traffic
What is iFrame traffic?
iFrames are web elements that allow the insertion of external content into a webpage (e.g. a social widget or a YouTube video). iFrame traffic is the sum total of the web traffic that those iFrames display.
How does iFrame traffic work?
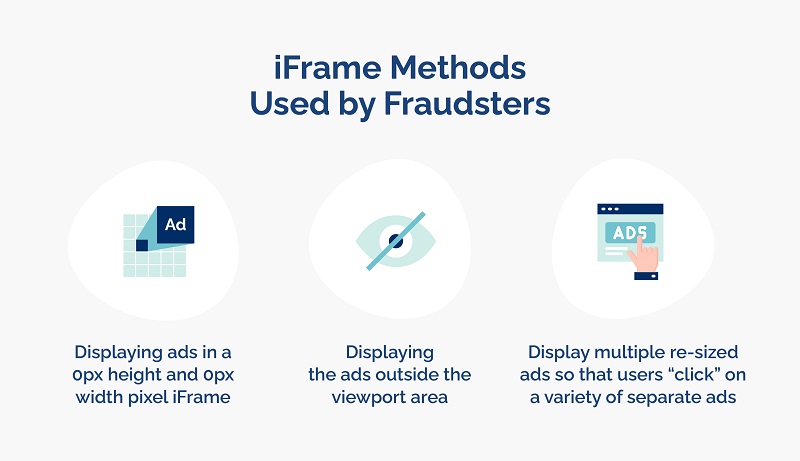
For instance, fraudsters can use iFrames to load entire pages in a window of 0 height and 0 width. This generates false visits as the users are not able to effectively see the content of the page.
Fraudsters can also load iFrames transparently over a web page. A fraudster could intercept a click made by a user on this top layer and use it for unintended purposes e.g. a purchase button.
What are the threats posed by iFrame traffic?
Traffic run on iFrames is not fraudulent, per se, and it’s a method that has valid use cases. However, it can pose a vulnerability when fraudsters use it to generate false visits, or to deceive the user into clicking something they don’t intend to.
iFrame traffic can drive impression fraud, click fraud, lead fraud, subscription fraud, and attribution fraud, and it can skew your analytics.
Related techniques: Clickjacking, ad stacking, and pixel stuffing.
Proxy traffic
What is proxy traffic?
Proxy traffic is web traffic that has passed through one or more different servers.
How does proxy traffic work?
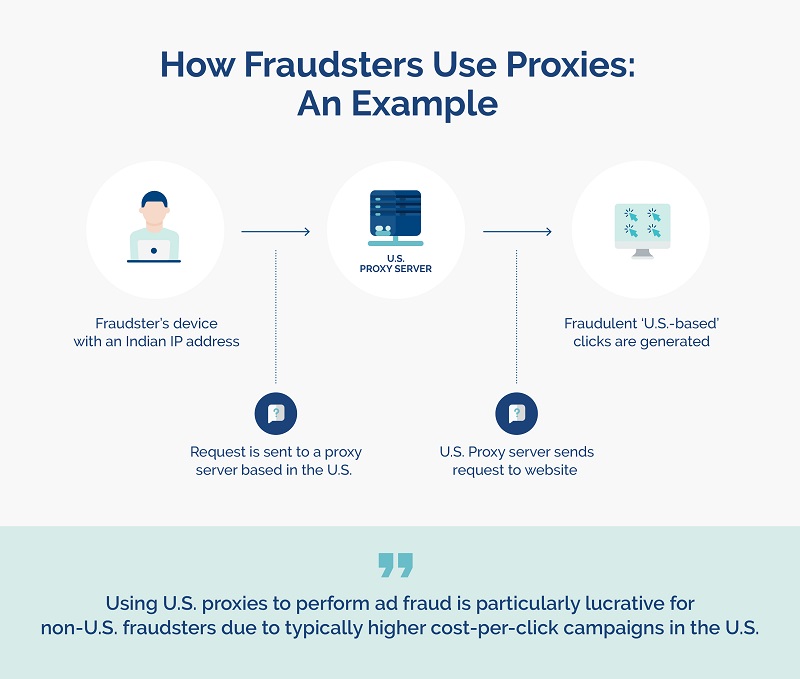
Specifically, fraudsters use proxy traffic to allow anonymous browsing by hiding the location of a user’s IP address in order to enable fraudulent activity.
As a result, this can cause advertisers to believe that their traffic is coming from high-tier countries, when in fact it’s coming from countries with lower-quality and less valuable traffic. This can result in them paying for leads they haven’t actually obtained.
What are the threats posed by proxy traffic?
Proxy traffic can drive impression fraud, click fraud, lead fraud, subscription fraud, attribution fraud, and skewed analytics.
Related techniques: Bad bots, geomasking, and datacenter traffic.
Click injections
What are click injections?
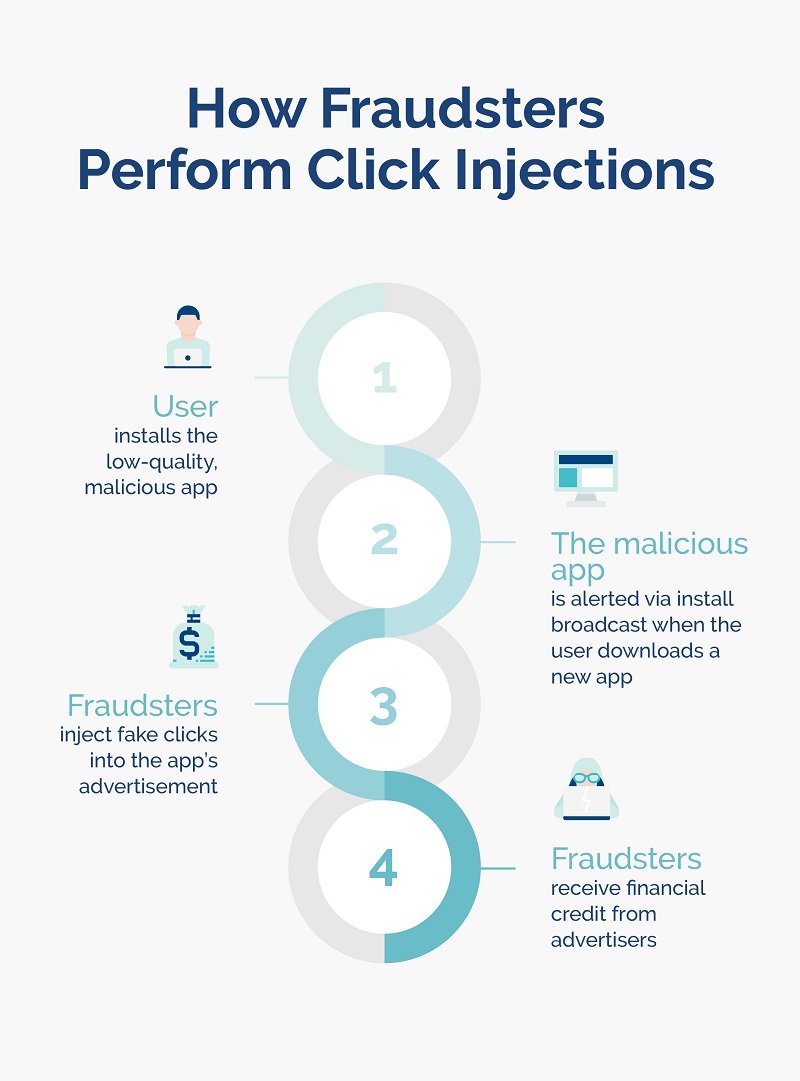
Click injections are a sophisticated type of click spamming affecting Android devices. Fraudsters publish or have access to a downloaded app that listens to “install broadcasts”, which notifies them the moment a new app starts downloading.
The fraudster then triggers the click right after the download finishes but before the user opens the app, which gives the impression that that click — the most recent one — delivered the download. As a result, they collect the attribution payout.
How do click injections work?
Typically, fraudsters use low-quality apps, such as apps that provide phone wallpapers, to infect devices. These apps can run in the background and appear “asleep” until the install broadcast informs it to generate clicks on a new download.
What are the threats posed by click injections?
Advertising budget loss, skewed data, and damage to advertisers’ segmentation of traffic are all threats posed by click injections. Since click injections directly infect devices, experts consider them quite a malicious form of ad fraud, and fraudsters find them easy to implement.
Related techniques: Malware.
Datacenter traffic
What is datacenter traffic?
In essence, data centers are large facilities that house networked computers that centralize organizations’ IT operations, including the processing, storing, and sharing of data. Data centers attract fraudsters because they can hide well within them, so analysts consider this non-compliant traffic.
How does datacenter traffic work?
Data centers have networks of servers that have their own IP addresses, and often organizations will provide a proxy service to their users. Typically, fraudsters route the bots they use through the proxy services to avoid detection via IP addresses.
What are the threats posed by datacenter traffic?
Datacenter traffic can cause impression fraud, click fraud, lead fraud, subscription fraud, attribution fraud, and can skew data and analytics.
A lot of datacenter traffic is not malicious and is simply registered as nonhuman traffic. However, investigators have uncovered several schemes where fraudsters load ads on fabricated websites and claim the falsified ad revenue.
Related techniques: Bad bots, malware, and proxy traffic.
Click spamming
What is click spamming?
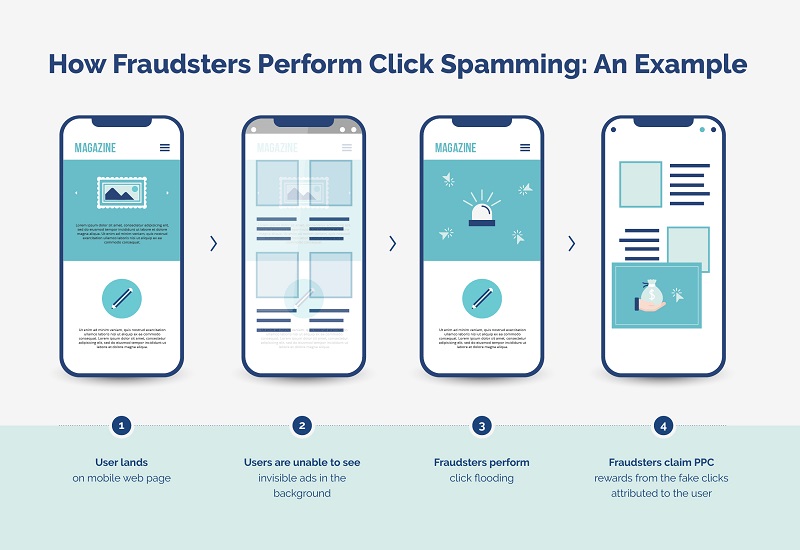
Click spamming occurs when fraudsters send a large number of low-quality fake clicks — (fraudsters call this click flooding) — to an ad in an attempt to fraudulently capture PPC budgets or obtain attribution before an action (such as an app installation).
How does click spamming work?
To carry out click spamming, fraudsters need users to open a webpage that the fraudster runs, or download a malicious app to their mobile device. The app or website will run an automated process, known as click bots, coded into it.
Once they do this, fraudsters can:
- Send out a flurry of fake clicks, usually to invisible ads, while the app is running
- Generate impression fraud via fake clicks, while the impressions appear to be real ad engagements
- Send clicks from users’ devices to random vendors, where they ultimately collect the payout on ads.
Fraudsters carry out these actions without the user’s knowledge or consent.
In cases of install-focused campaigns, when fraudsters are successful in obtaining the last click, they then receive attribution for the installation, including the paid commission. As a useful standard in the industry, analysts consider 75% of app installs “organic” if they occur within an hour of the click, and 94% organic if they occur within 24 hours of the click. In other words, anything outside of these parameters might be an indication of click spamming.
What are the threats posed by click spamming?
In terms of maliciousness, click spamming isn’t the worst form of ad fraud, but it does drain organizations’ budgets both quickly and easily, and deeply skews marketing data. It’s also not constricted to any geographical location and affects all types of organizations.
Related techniques: Botnets, click farms, bad bots, and data traffic.
Ad stacking
What is ad stacking?
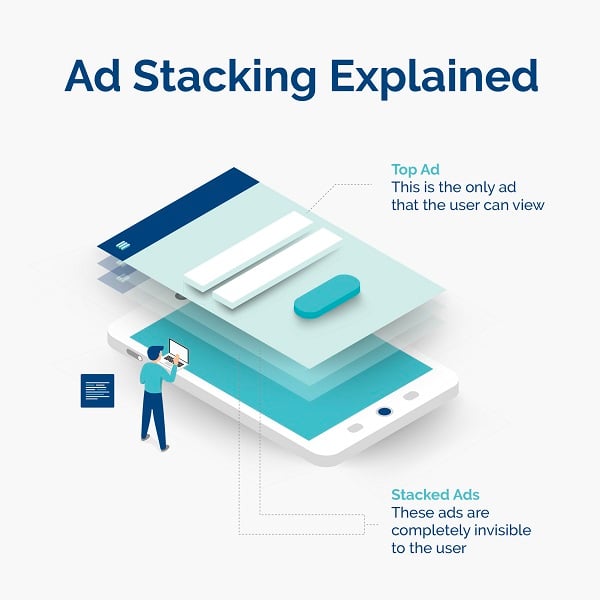
Ad stacking occurs when fraudsters stack multiple ads on top of one another in a single ad placement. In practice, the top ad is the only one visible to the user, yet the platform bills advertisers for all the false ad impressions and clicks from the ads underneath.
How does ad stacking work?
Fraudsters create a website and make advertising space available on it. Fraudsters then join ad exchanges to sell advertising spaces. Once fraudsters buy the ad space, they load multiple invisible ads on top of one another, and advertisers end up paying for the fake impressions those ads generate.
What are the threats posed by ad stacking?
Ad stacking isn’t as nefarious as other ad fraud techniques and is moderately difficult for fraudsters to achieve. However, like many other ad fraud techniques, ad stacking drains budgets quickly, causes fake impressions, and leads to misrepresented campaign data and analytics. Overall, it applies to almost all geographies and verticals.
Related techniques: Bad bots, botnets, malware, and iframe traffic.
Geomasking
What is geomasking?
Geomasking occurs when fraudsters hide the location of the leads they generate. Since ad campaigns often have different ad spends for different locations (for example, a lead might be worth more coming from the U.S. than from Brazil), fraudsters spoof IP addresses to make leads and traffic appear more valuable than they actually are. Basically, advertisers pay out for high-quality leads, in return for low-quality traffic.
How does geomasking work?
Fraudsters spoof IP addresses to hide the real identity and location of the fraudster, and to appear as an identity aligned with the ad targeting of the advertiser.
What are the threats posed by geomasking?
Geomasking can drive impression fraud, click fraud, lead fraud, subscription fraud, and attribution fraud, and it can skew your data and analytics.
Campaigns that succumb to geomasking practices can see their budgets quickly drained.
Related techniques: Bad bots, botnets, malware, click spamming, click farms, datacenter traffic, and proxy traffic.
Pixel stuffing

What is pixel stuffing?
Pixel stuffing is the act of stuffing multiple ads into pixels so small that human users can’t detect them. Although the human eye can’t see them, these illegitimate ads still generate impressions from real users.
How does pixel stuffing work?
First, fraudsters build a website and join an ad exchange to deliver and display ads as a publisher. Next, they compress ads into 1×1 pixel frames on the website, and often use bad bots to create fake impressions, clicks, or leads to sell onto an ad exchange. In the end, fraudsters cash out on the profit those fraudulent impressions generate.
What are the threats posed by pixel stuffing?
Although pixel stuffing isn’t a particularly malicious ad fraud technique, advertisers still end up paying for impressions nobody ever sees, plus skewed analytics and missed targets. Pixel stuffing is a relatively difficult ad fraud technique to carry out, but fraudsters use it all over the world.
Related techniques: Iframe traffic, bad bots, botnets, malware, geomasking, proxy traffic, and datacenter traffic.
Know your enemy: stopping ad fraud techniques
If you don’t know which types of ad fraud are affecting your organization, you can’t know how to best protect your organization from them.
Why manual methods can’t stop ad fraud techniques
Some organizations use manual methods to protect against the effects of several ad fraud techniques. However, manual methods are inadequate when it comes to protecting your organization. The only reliable and secure way to detect and mitigate ad fraud is to enlist the use of an anti-fraud solution.
How Opticks stops ad fraud techniques automatically
For example, anti-fraud solution Opticks:
- Uses machine learning to identify reproduced patterns and apply algorithms to detect new bad bot patterns
- Filters traffic identified as click farm activity to prevent it from depleting your campaign budgets
- Detects fraudulent traffic by looking at existing traffic data and analyzing the behavior on ads to compare it with real-time activity — when it detects anomalies, it can quickly and automatically prevent fraudulent traffic from affecting campaigns
Plus, while some ad fraud techniques are more widespread and common than others, organizations must be aware of the types of ad fraud that can affect their specific use case. In some instances, location can also correlate with certain types of ad fraud.
To find out more about how we can work together to prevent ad fraud from destroying your ad campaigns, click here to request a free Opticks demo or start your own free trial.
Comments
7 responses to “Ad Fraud Techniques 101: The Complete Guide to Ad Fraud”
[…] Despite constant efforts to stop it, the ad fraud impact on agencies keeps growing, and malicious ad fraud practices remain a persistent problem for everyone in the […]
[…] a complete understanding of the extent of ad fraud, including the types of ad fraud that exist, how they relate to your business and industry, and the damage it can cause, is key to […]
[…] To protect your ad spend: Anti-ad fraud solutions stop fraudsters from siphoning off your budget by detecting and preventing tactics such as fraudulent redirects, bots, and click spamming. […]
[…] infected apps or browser extensions, often paired with click spamming, fraudsters can inject ads into websites and apps without the user knowing. You can usually spot […]
[…] Ads click fraud is an ad fraud technique where bad actors fraudulently click on paid Google Ads with no intention of buying anything or […]
[…] as a vehicle to trick users into clicking something they don’t intend to (also known as clickjacking), or to load a page hidden from the user behind a very small iframe. You can apply certain […]
[…] If you suspect fraudsters are hitting your campaigns with bad proxy traffic, it’s time to act. Find out more about how the expert team at Opticks can help protect your advertising campaigns by booking a free product demo or starting your free trial. For a deeper look at how this technique fits alongside other threats, see our guide to ad fraud techniques. […]